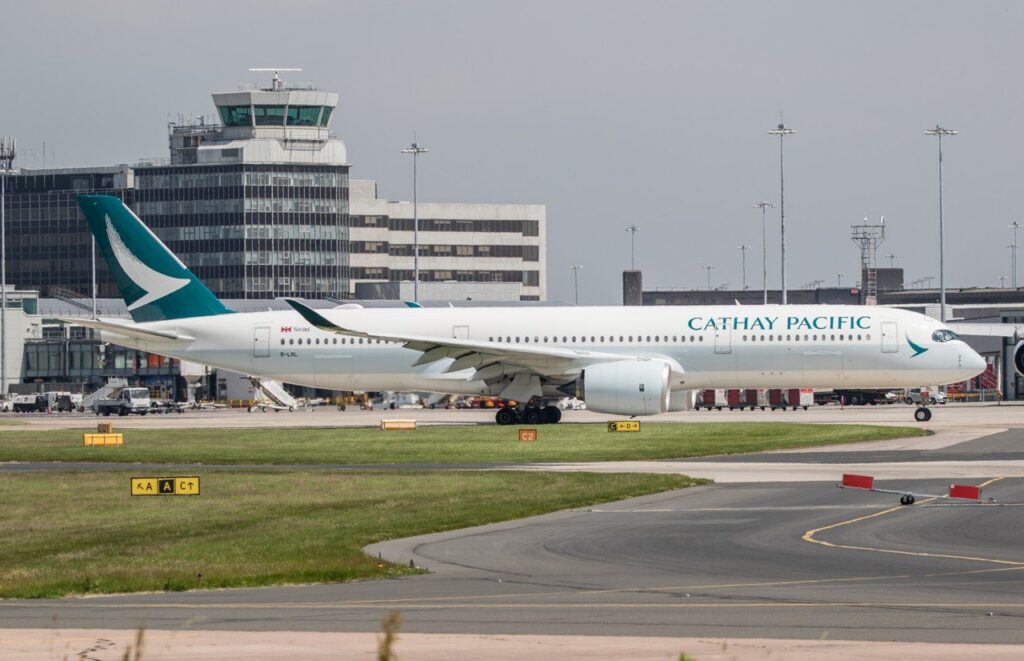
Cathay Pacific Airbus A350, June 17, 2017. Archive photo: Transport Pixels / Wikimedia Commons, CC BY 2.0. Resized.
About 53,000 Cathay Pacific bookings were affected by unauthorized access to travel-reservation data at technology supplier Amadeus, the airline disclosed Friday, with passenger names and flight details among the information exposed.
Cathay said in its October 30 security notice that Amadeus notified it on October 28 and provided further details October 29. The unauthorized party used login credentials assigned to an Amadeus system account, the airline said.
The figure concerns bookings, not a confirmed count of individual passengers. Cathay said its own systems and operations were not affected.
Names, booking references and flight details accessed
In most cases, the accessed information included booking references, passenger names and flight details, according to data Amadeus supplied to Cathay.
A smaller subset of records potentially included additional personal information, such as email addresses, phone contacts, travel-document information or frequent-flyer numbers. The airline did not publish a separate count for that subset.
Cathay said there was no evidence financial or payment information had been accessed. It also said Amadeus had not identified evidence of misuse of the affected data to date.
Those findings describe what the companies had established so far. They do not mean every category of personal data was unaffected or that the investigation was complete.
Supplier resets password and increases monitoring
Amadeus told Cathay it had taken steps to contain the incident, including a password reset and enhanced monitoring and detection capabilities, the airline said.
Cathay said it had informed the relevant authorities and was continuing to analyze the information provided by Amadeus. It plans to notify affected customers individually after establishing the relevant details.
The carrier’s notice describes unauthorized access in the supplier’s system occurring between August 2023 and September 2026. Friday’s disclosure does not describe a new intrusion into Cathay’s systems that day.
Another airline discloses reservation-data exposure
Japan’s Star Flyer separately said in an October 30 update that it had received an updated report through All Nippon Airways concerning unauthorized access to reservation information in the Amadeus passenger-service system it uses.
Star Flyer said there were indications that some customer information may have been accessed, including names, booking references, travel dates, routing, contact details, frequent-flyer numbers and ticket or seat information. It said it was still verifying the number of people affected.
The Japanese airline said credit-card numbers and account passwords were not involved. It said compromised authentication credentials had been revoked and monitoring strengthened.
Neither airline notice gives a total for all airlines or passengers affected by the supplier incident. Cathay’s approximately 53,000 affected bookings should not be read as that broader total.
JBizNews Global Desk | HONG KONG
© JBizNews.com. All rights reserved. Unauthorized reproduction or redistribution is strictly prohibited.