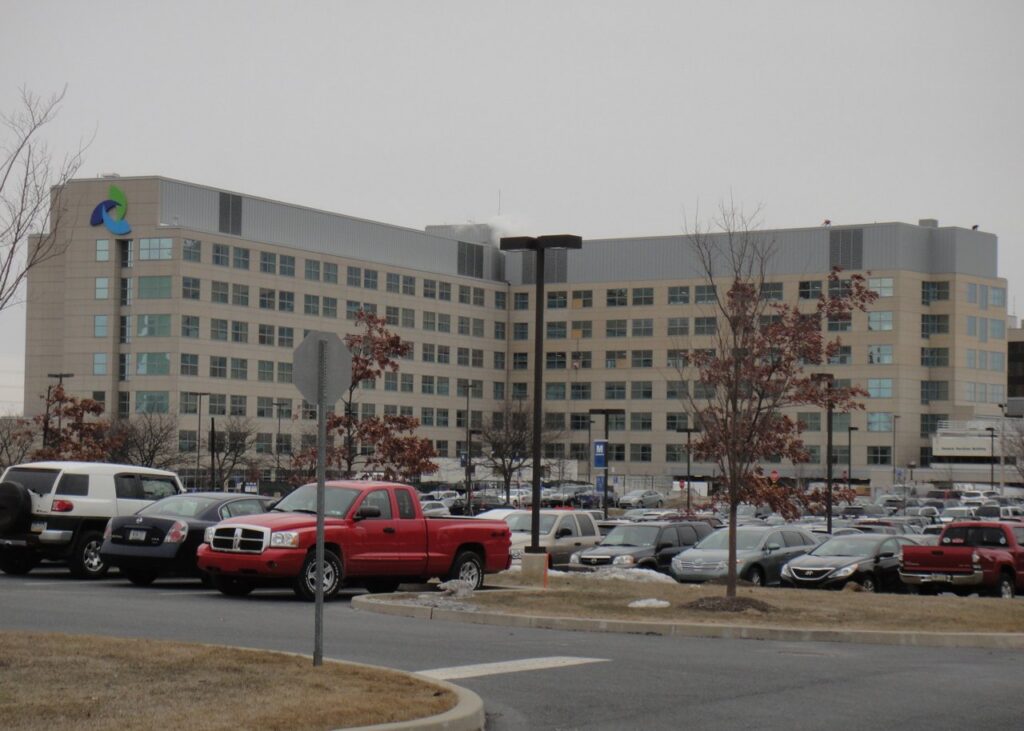
Archive photo: Lehigh Valley Hospital in Pennsylvania, March 2014. CyberXRef / CC BY-SA 3.0; cropped.
Lehigh Valley Health Network paid $800,000 and agreed to three years of federal oversight under a ransomware-related HIPAA settlement announced Thursday by the Department of Health and Human Services.
The October 29 announcement from HHS’ Office for Civil Rights concerns an investigation into a 2023 breach, not a newly reported cyberattack. HHS said the settlement with the Pennsylvania health system and its affiliated covered entities resolves potential violations of the HIPAA Privacy, Security and Breach Notification Rules.
According to HHS, the attack affected protected health information belonging to 248,359 people. Information was taken from the network and posted on the dark web. The agency said the exposed material included sensitive photographs of cancer patients receiving radiation oncology treatment, alongside personal, financial and medical information.
A 2023 breach, a settlement announced today
The health system reported the breach to HHS on May 15, 2023. Its report said suspicious activity discovered on February 4 of that year was subsequently determined to be ransomware, according to the agency.
HHS said its investigation identified potential failures to conduct an accurate and thorough assessment of risks to electronic protected health information and to implement procedures for regularly reviewing system activity. Such reviews include audit logs, access reports and security-incident tracking records.
The agency also identified potential impermissible disclosure of patients’ protected health information and failures to notify affected people and HHS in a timely manner. These are the potential violations addressed by the settlement, rather than a report of a new incident or a new finding about the condition of the network’s systems today.
What the three-year plan requires
Under the corrective action plan, which OCR will monitor for three years, LVHN committed to a thorough risk analysis and a risk management plan addressing identified security risks and vulnerabilities.
The health system also agreed to review its privacy, security and breach-notification policies and procedures and revise them where needed to comply with HIPAA. It will review and, as necessary, develop or revise HIPAA training materials for workforce members according to their duties.
OCR described the agreement as its 22nd ransomware enforcement action. Director Paula M. Stannard said failure to assess risks thoroughly and regularly review system activity makes regulated organizations attractive targets for cyberattacks.
For hospitals, nursing facilities and other organizations handling protected health information, the announcement puts the focus on controls that precede an attack as well as notifications that follow one. OCR’s accompanying recommendations call for organizations to identify where electronic patient information is held and how it moves through their systems, keep risk analyses current, maintain audit controls and regularly review system activity.
The agency also recommends access-authentication measures, encryption in transit and at rest when appropriate, and workforce training specific to employees’ roles. The settlement’s new development is the $800,000 payment and monitored corrective action plan announced October 29; the underlying ransomware incident dates to 2023.
JBizNews Desk | Washington
© JBizNews.com. All rights reserved. Unauthorized reproduction or redistribution is strictly prohibited.