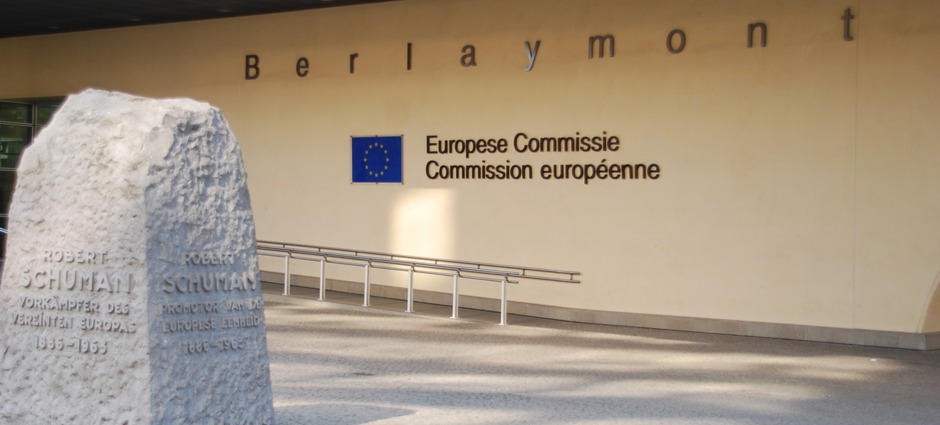
Berlaymont entrance, 2011 archive. Matthias v.d. Elbe / CC BY-SA 3.0. Cropped; same license.
The European Commission confirmed Thursday that a cyberattack using an artificial intelligence tool had targeted its internal systems, disrupting access to staff services while investigators examined whether personal information was compromised.
The attack was detected and confirmed on October 22, Commission digital spokesperson Thomas Regnier told reporters Thursday. The confirmation concerns an attack first identified last month, not one that began Thursday.
“The investigation is still ongoing. We are taking any necessary steps based on the findings as they come,” Regnier said at the briefing. “We have not detected any evidence of a data breach affecting Commission staff as a whole.” His comments left the extent of any compromise unresolved, rather than establishing that no individual’s information could have been affected.
The Commission took several internal applications offline as a precaution, and most had since been restored. Regnier declined to identify who was responsible or confirm whether the attack was over. He said the Commission had received no ransomware demand.
The disruption affected staff tools used for salary information, leave requests, timesheets and other personnel services. The Sysper human-resources platform was working again Thursday, while the staff health-insurance system remained unavailable, according to two EU officials familiar with the situation. Those operational details were separate from Regnier’s public remarks.
The affected platforms hold sensitive employee information, making the investigation important beyond the temporary loss of access. Investigators had not publicly established a staff-wide data breach, the attacker’s identity or full recovery. The Commission’s digital services department was assessing the damage, and the EU institutions’ cybersecurity service and the European Data Protection Supervisor had been informed.
JBizNews Desk | Brussels
© JBizNews.com. All rights reserved. Unauthorized reproduction or redistribution is strictly prohibited.