When hackers drained $6.3 billion from Binance, the world’s largest cryptocurrency exchange, on October 29, it was tempting to treat it as a crypto problem. Less than a week later, Crédit Mutuel Arkéa, a French lender, disclosed that hackers had made off with roughly €100 million ($112 million).
The back-to-back attacks highlight the threat of cyber heists to traditional banks. “If a company like Binance can lose billions of dollars, the threats facing banks are overwhelming,” said Ryan Kirkley, cofounder and CEO of Global Settlement, which develops blockchain infrastructure for banks. Speaking at the Digital Asset Summit in London on November 10, he said: “It is impossible for the average bank to stay secure.”
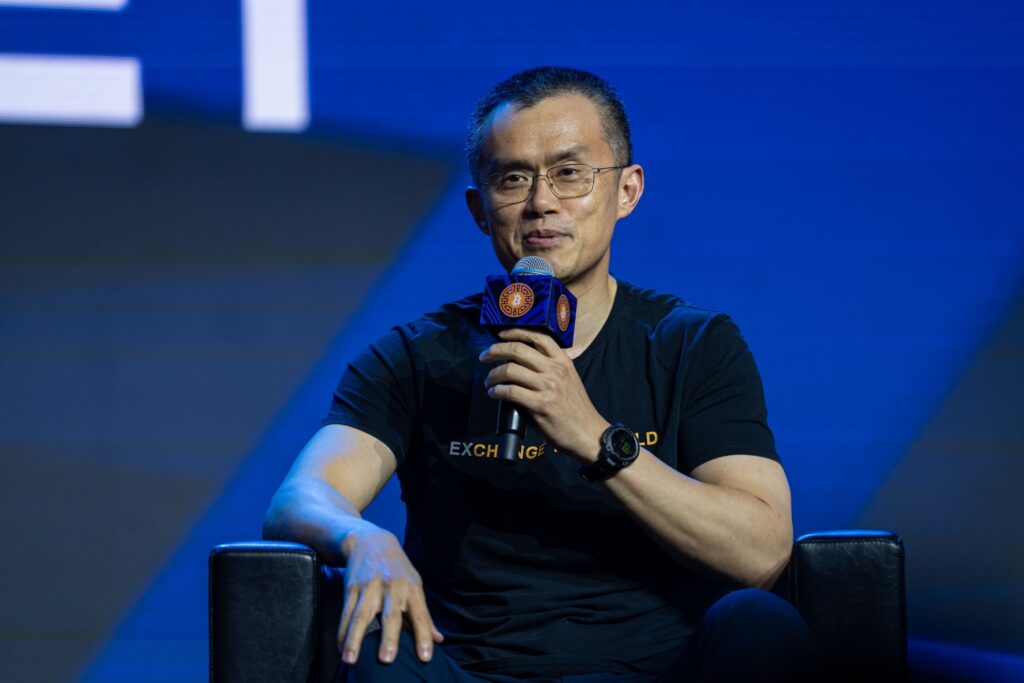
Binance’s founder and former CEO, Changpeng Zhao, went further. “If a crypto exchange can be hacked, banks are in a worse position, in my opinion,” he told CoinDesk days after the heist.
The Binance hackers used a combination of social engineering and malicious software to take over crypto wallets and drain them of funds. This involved arranging a series of fake job interviews to persuade a Binance engineer to inadvertently download malware which allowed the hackers into the company’s systems.
The FBI has seized $1.2 billion of the stolen cryptocurrency, while Binance confirmed it had “replenished” approximately 98% of the total impacted amount.
The weaknesses hackers exploited to steal funds on Binance are not unique to crypto and the same vulnerabilities are present in traditional financial institutions, said Katerina Mitrokotsa, professor of cybersecurity at the University of St. Gallen in Switzerland. “Banks are not automatically safer just because they are regulated.”
Regulators on both sides of the Atlantic have raised concerns. In the U.S., the Federal Reserve and the Office of the Comptroller of the Currency began calling banks on November 2 to ask about unusual activity and service disruptions, Reuters reported.
In July, the European Central Bank wrote to the chief executives of 110 banks warning about the risks of frontier AI models, which are making it “quicker and cheaper to identify and exploit vulnerabilities in IT systems.” .
Banks have some advantages over crypto platforms, according to Vivien Mura, chief technology officer of Orange Cyberdefense, the cybersecurity arm of French telecoms group Orange. The EU’s Digital Operational Resilience Act, or DORA, which has applied since January 2025, requires banks to test their defenses and report cyber incidents. “They also benefit from mechanisms crypto platforms lack, such as the ability to block or reverse payments and close cooperation with supervisors and law enforcement,” Mura said.
Yet he acknowledges that those advantages only go so far. “Banks are better placed to absorb and recover from a major attack, but they are not necessarily better at preventing one.”
Mitrokotsa highlights two weak spots: The long chain of outside suppliers banks rely on, which DORA tries to address by bringing the most critical providers under direct EU supervision, and the aging technology many banks still run.
In the Crédit Mutuel Arkéa case, hackers used the bank’s own account to carry out transactions after gaining access through an unnamed service provider. The bank told customers the incident had “no impact” on their assets.
“Compromised suppliers, staff with privileged access, fake job approaches and the misuse of internal tools have been recognized risks for years and are not unique to any one sector,” Lee Elliott, director of resilience and cyber at UK Finance, the British banking industry body, told Fortune.
Banks benefit from the sector’s practice of sharing threat intelligence through initiatives such as the Financial Sector Cyber Collaboration Centre, he adds.
Attackers are already exploiting Europe’s aging IT systems. Since October, hackers have hijacked internet-connected refrigeration systems at supermarkets in more than a dozen countries and at three French blood banks. Danfoss, which made the electronic temperature controllers, has said most affected units were older models that no longer receive security updates.
“A fridge doesn’t look like a security risk, and that’s exactly why attackers like it,” Mitrokotsa says. “Banks have the same problem. Many still run core systems that are decades old, next to old servers, building control systems and suppliers’ remote access.” Her advice is for banks to start by knowing every device connected to their networks, then make sure that the ones with no need to reach core systems are cut off from them.
Banks could even learn from crypto, Mitrokotsa added. “Some exchanges split control of a key between several parties, so no single computer can approve a transfer on its own, much like a vault that needs two keys turned at once. An attacker who compromises one laptop gets only part of what they need.”
Personal AI agents also present a new risk for financial institutions to grapple with. Increasingly, consumers are using digital assistants—such as Meta’s Muse—to make purchases or pay bills on their behalf.
Citigroup and Bank of America have restricted agents from accessing customer accounts., JPMorgan Chase chief executive Jamie Dimon has urged financial institutions not to allow autonomous AI agents to handle banking payments, warning of their “treacherous” risk. U.K. banks HSBC, Nationwide, NatWest, Barclays, and Lloyds have also blocked AI agents from accessing their accounts. However, some European lenders are taking a more cautious middle path. Santander and ING let agents make payments, but only within limits the customer sets in advance or after the customer approves each purchase.
With the number of cyber threats mounting, the Crédit Mutuel Arkéa hack is unlikely to be the last attack on Europe’s financial sector.
This story was originally featured on Fortune.com