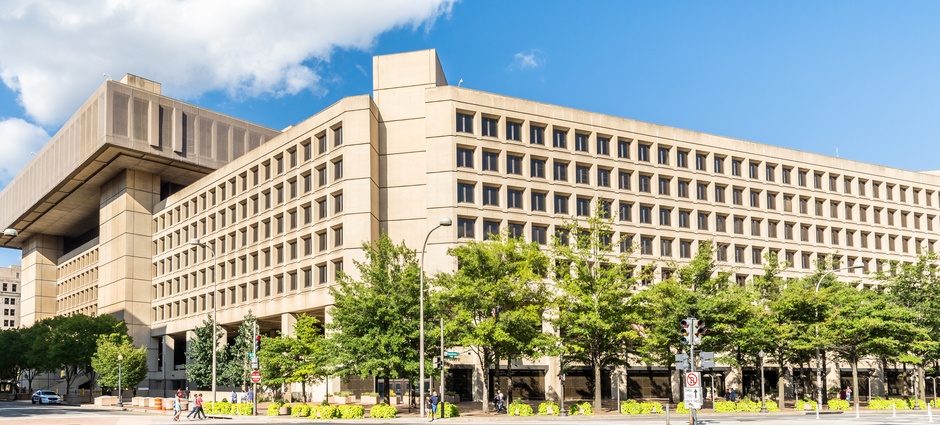
File photo: The J. Edgar Hoover Building in Washington, September 7, 2019. dconvertini / Wikimedia Commons / CC BY-SA 2.0; cropped and resized. Adapted image: CC BY-SA 2.0.
The Justice Department said Thursday that an international operation removed Gootloader malware from more than 100 computer servers and seized U.S. domain names used to deliver and control the malicious software.
The operation targeted infrastructure behind a malware network that has infected at least 25,000 computers worldwide since 2018, according to the department. Gootloader has been used in ransomware attacks against at least 44 U.S. victims, resulting in approximately $28.8 million in losses, officials said.
Some of the cleaned servers hosted compromised WordPress websites. The operation was carried out with court authorization by the Justice Department, FBI and international partners, the department said.
Gootloader can trick people into downloading malicious files, then add their computers to a network of compromised machines known as a botnet. The operators used that network to infect other computers and sell access to ransomware criminals, according to warrants unsealed this week.
The Defense Criminal Investigative Service said targets included the U.S. Department of War and defense-industry organizations. The department did not name the affected organizations or say that every infected computer had been cleaned.
The Shadowserver Foundation helped internet service providers and computer-security response teams identify infected systems, notify victims and support remediation. Those steps are distinct from removing malware from the more than 100 servers identified in the operation.
The effort was coordinated with Operation Endgame, a multinational initiative targeting malware services. Investigators from Germany, the Netherlands, Canada, Denmark, France, the United Kingdom, Australia and Europol took part alongside U.S. authorities.
For businesses, the case shows how compromised websites can become a route for criminals to obtain access to company computers. Thursday's announcement concerns a disruption of that delivery infrastructure, not a finding that ransomware has been eliminated or that every past victim has recovered.
© JBizNews.com. All rights reserved. Unauthorized reproduction or redistribution is strictly prohibited.